root@hamcodes: authorized use only

No fluff. No theory. Just execution.

how_to_hack_all_tech --practical --now

A field guide for operators who would rather run the command than read another chapter about it. Real tools, real syntax, real playbooks. Then two free courses you can start in this tab.
Red, blue and purple 2 free courses No sign-up
The Hacker's Notes, the book
night_shift --3d --interactive

Night Shift at Veltrix

A 3D security simulation you actually operate. Cover the late shift in accounts payable at a freight company: a real desktop of twenty apps, a mobile and a desk phone, and the attacks that really breach companies. No install, no sign-up, and nothing you do leaves your browser.
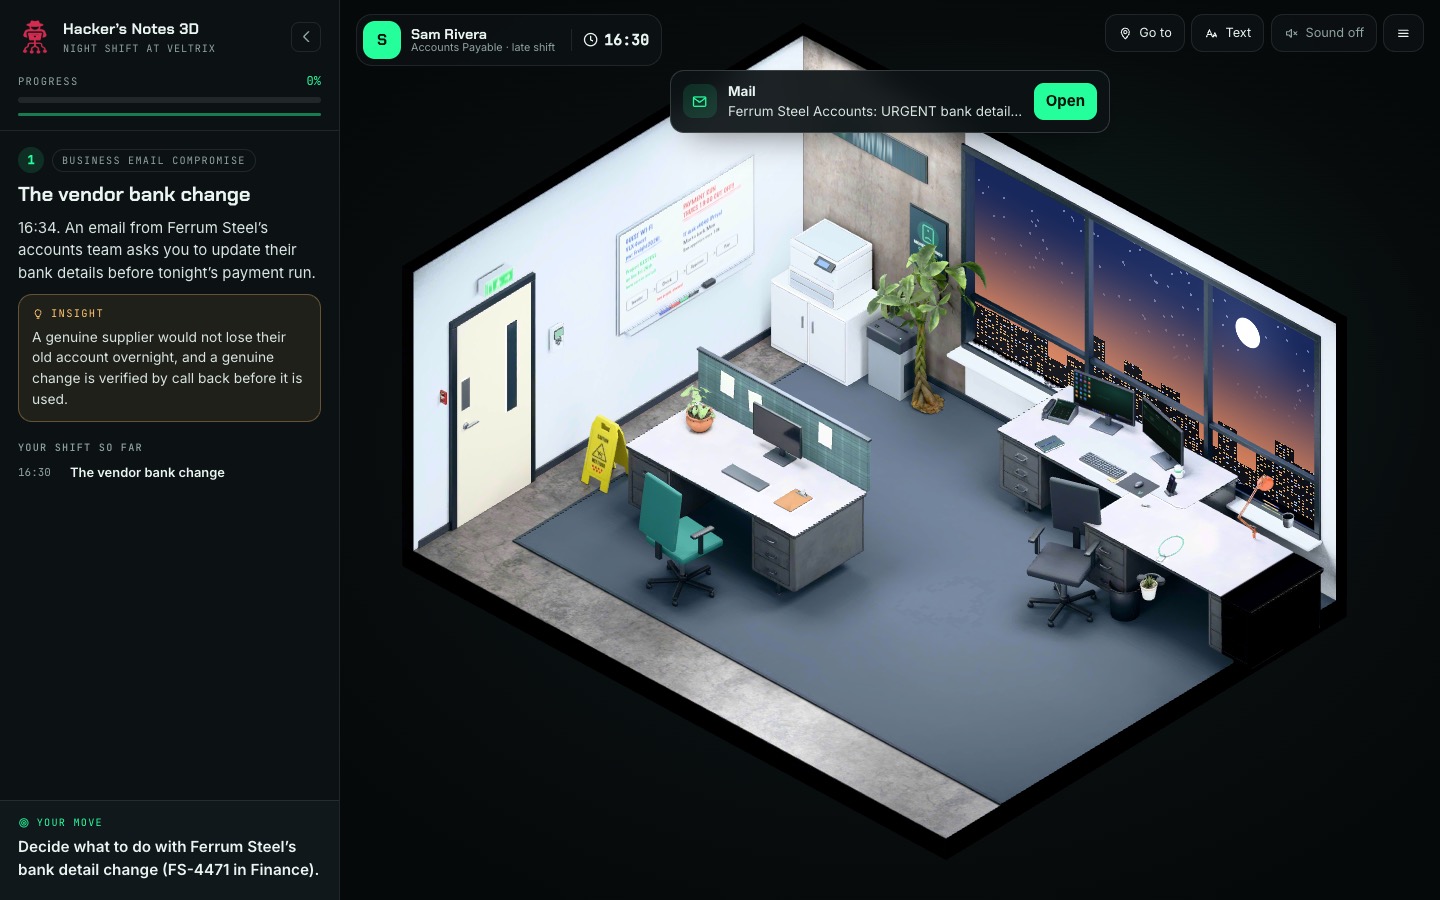
01Business email compromiseA supplier asks to change their bank details before the payment run closes.
02MFA fatigue & vishingYour phone floods with sign-in prompts, then a voice claiming to be IT calls.
03Prompt injectionA vendor PDF quietly tells your AI assistant to forward the finance mailbox.
veltrix_logistics: accounts payable, late shift
A freight company's finance office at night, rendered in 3D Live 3D exercise Tap to see how it works

Best on a laptop. Eight scenarios, six per shift, seeded so every run is different. A real computer and a real phone, not buttons on a video.

Open the full sim
hackers_python

Learn Python by building security tools

Real Python, in your browser, right now. No install and no sign-up. Four sections, 32 lessons, and a finished tool you keep at the end of each one.

01Password checkerScore a credential on length and character classes.
02Login detectorParse an auth log and flag brute-force attempts.
03Credential triageRate a whole dump and print a report.
section_01: fundamentals through a security lens

Section 1 is playable above. Progress saves by itself and carries over.

Play all 4 sections
free_course

Hack your cyber career

Ten modules, free, no sign-up. A career roadmap with the diagrams and over 180 checked links behind it: free training, free certifications, labs, books and job boards. Pick a lane, build proof instead of a wish list, and handle the interview.

Free to read, nothing to install, no email required.

Start the free course
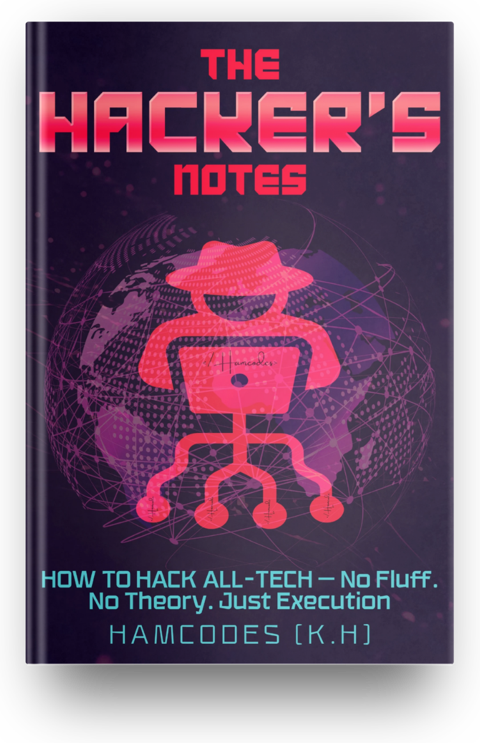
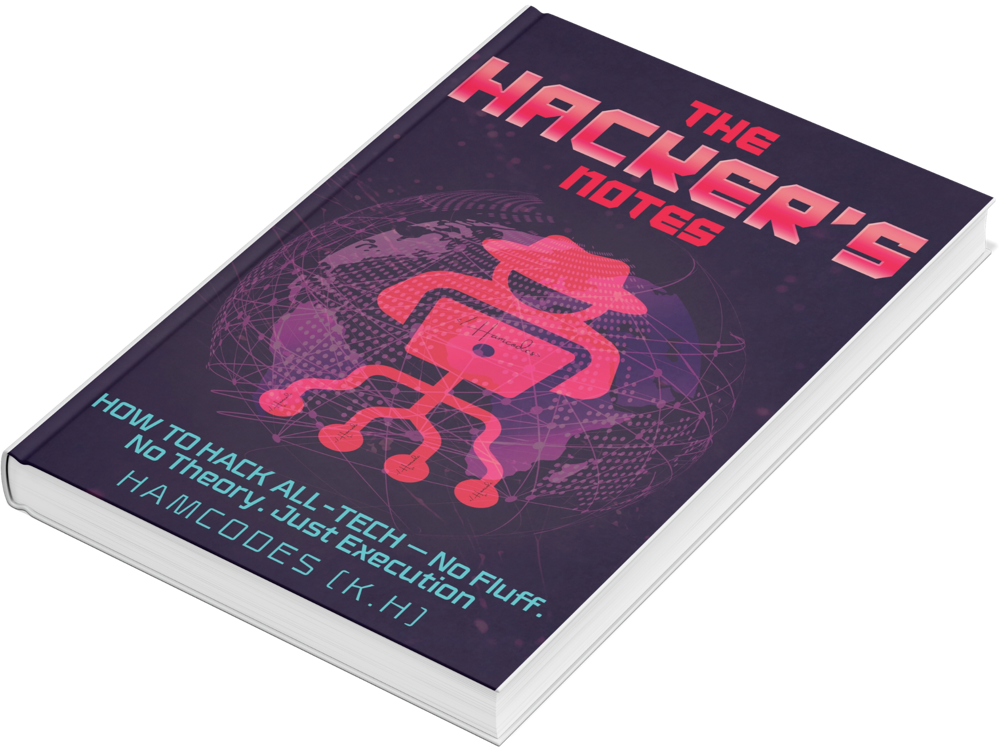
The Hacker's Notes cover
the_field_guide

How to Hack All-Tech

The book the rest of this site came out of

A streamlined, field-tested guide focused on what you actually do. Every chapter ships command-line syntax and real tool usage, updated for 2025 systems and toolchains.

  • Direct execution. Skip the theory, start at the hands-on step.
  • Toolkits that run. Scripts, commands and playbooks for red and blue.
  • Modern coverage. AI and ML, blockchain, cloud, mobile and IoT.
  • Live examples. Real syntax and real tool usage in every chapter.
OSINT Exploitation Privilege escalation Evasion Incident response Threat hunting AI / ML Cloud IoT

Paperback and Kindle. For training, simulation and authorized environments only.

FREE RESOURCE - NO CERT NEEDED

The Complete
Hacker's Methodology
From Recon to Root

Every phase. Every technique. Real tools. Zero fluff.

Get the full methodology - free.

Drop your email and confirm it. The complete guide unlocks on its own page. No waiting. No PDF to download. Just the knowledge.

  • All 6 attack phases with real techniques and tools
  • 100+ offensive techniques mapped to MITRE ATT&CK
  • Key tools for each phase: Nmap, BloodHound, Mimikatz, and more
  • AD attack paths: Kerberoasting, DCSync, PetitPotam, Golden Tickets
  • Built from real grind - not recycled Medium posts

No spam. I share my notes, not your data.

CHECK YOUR INBOX

We sent a confirmation link to . Click it and the full methodology opens.

Don't see it? Check spam / promotions.

WHAT'S INSIDE
PHASE 01
RECONNAISSANCE
OSINTGoogle DorksGitHub DorksSubdomain EnumPort Scanning████████████████████
PHASE 02
ENUMERATION
FTP(21)SSH(22)SMB(445)MSSQLAD Enum█████████████████████
PHASE 03
EXPLOITATION
SQLiXSSLFI/RFISSTI█████████████████████████
PHASE 04
POST-EXPLOITATION
SUID/GUIDSudo Abuse█████████████████████████
PHASE 05
LATERAL MOVEMENT
Pass-the-Hash█████████████████████████
PHASE 06
PERSISTENCE
█████████████████████████████████
hacker_in_the_shadows

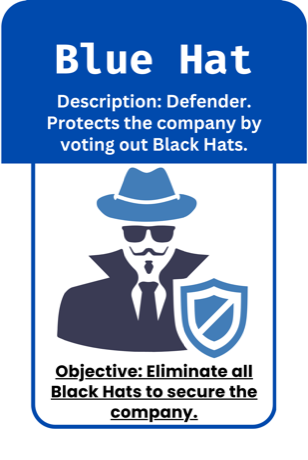
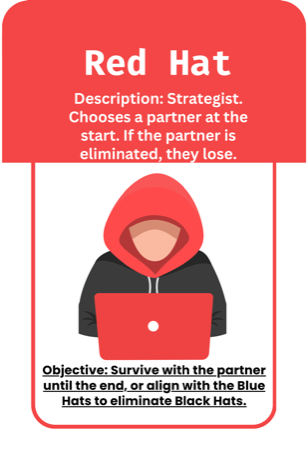
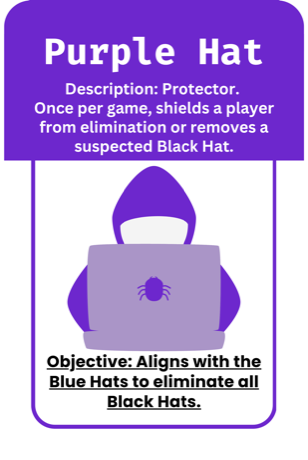
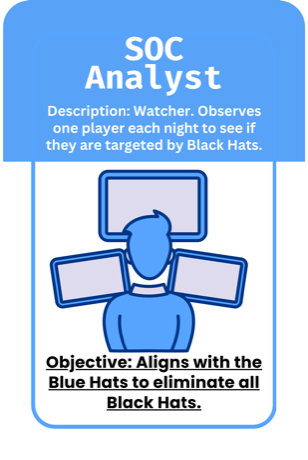
Play werewolf like a hacker

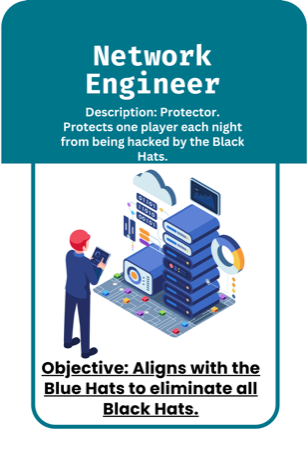
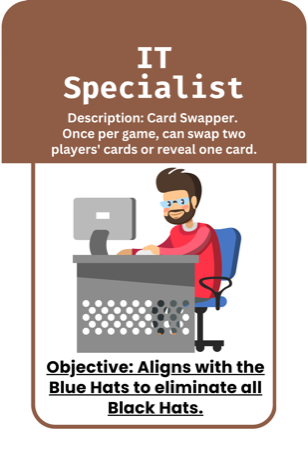
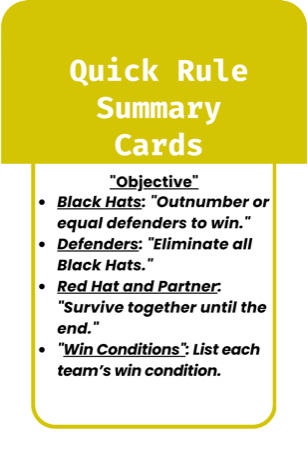
Two minutes to learn, fifteen to play. A social deduction card game where cybersecurity roles fight for control of the network. Anyone at the table could be the traitor.
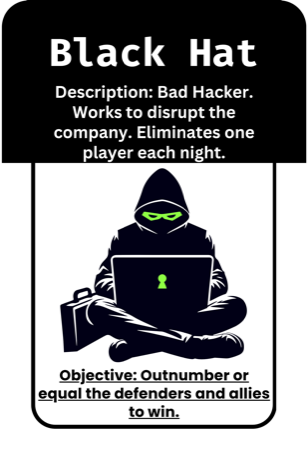
01Assign rolesEveryone draws a secret cybersecurity role.
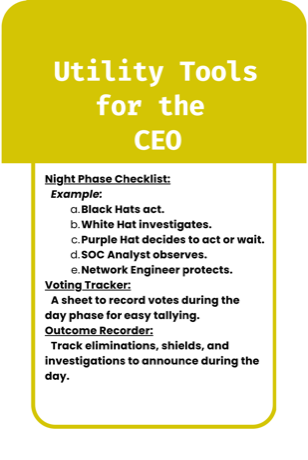
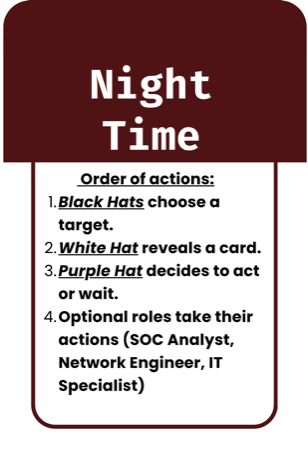
02Night phaseHidden hacks, investigations and defences resolve.
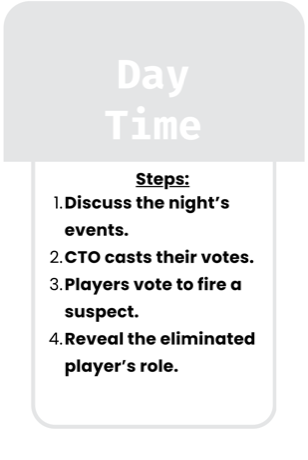
03Day phaseThe table debates, votes, and hunts the infiltrator.
Role card Role card Role card Role card Role card Role card Role card Role card Role card Role card Role card Role card Role card Role card Role card
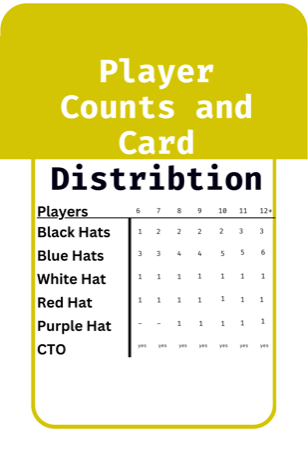
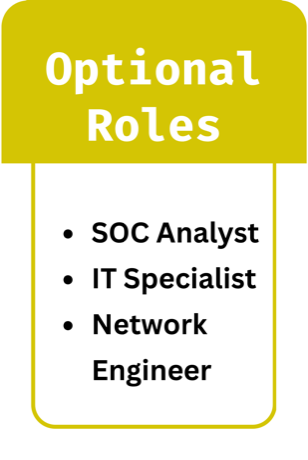
Black Hat White Hat CTO Purple Hats 30+ role cards
Order the card game
hacking_tees

Hacking Tees

Fifty-odd terminal-inspired tees for red teamers, devs, sysadmins and anyone who lives in a shell and would rather wear it too.
Scroll the drop →
Hacking tee design Hacking tee design Hacking tee design Hacking tee design Hacking tee design Hacking tee design Hacking tee design Hacking tee design Hacking tee design Hacking tee design
On hamcodes.com Shop the tees
hamcodes_gear

Hamcodes Gear

Hoodies, hats, sweatshirts and the rest, for coders, hackers and anyone who builds the thing rather than talking about it.
Scroll the gear →
Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear Hamcodes gear
On hamcodes.com Shop the gear
Who this is for

Whichever side of the wire you are on

Red teamOffensive operators
Blue teamDefenders and threat hunters
Penetration testersExploitation and escalation
SOC analystsDetection and response
StudentsLearning it by doing it
Ethical hackersInfoSec on your own time